How The Global Risks Alliance (GRA) is designing its community: a public digital layer open to anyone today, and an institutional layer of bylaws, membership terms, councils and working groups that opens only when its rules are adopted. Both run under one set of conduct, competition and correction rules.
Key takeaways
- The Global Risks Alliance (GRA) is designing the GRA community model in two layers: a digital layer of public pages, publications and enquiry routes that anyone can use today, and an institutional layer of bylaws, membership terms, councils and working groups that opens only when its rules are adopted [1, 2].
- The order is deliberate: records first, then rights. No member right exists before the instruments that create it, and no member count, partner or fee is published without a dated, sourced record [2, 1].
- Both layers run under the same rules: a written competition policy for every exchange, a conduct code with a fair complaint process open to anyone, and corrections as recorded versions [3, 4, 5].
- A community for systemic risk has to reach beyond the connected: 6 billion people are online in 2025, but 2.2 billion are not, and only 23% of people in low-income countries use the internet [6].
- Within the wider programme, participation is recorded in the programme’s participation records and in NXS-RLS (participants, agreements and handoffs), and the Nexus Universe application has its home at universe.nexus [7, 8].
What the GRA community model is
The GRA community model is the design by which financial institutions, professionals and the public take part in GRA’s work: a digital layer of public information, publications, enquiry and correction routes that serves anyone, and an institutional layer of bylaws, membership terms, industry councils, sector platforms, working groups and learning that serves members once its rules are adopted [1, 2]. As its home page states, GRA is a nonprofit business league for the financial services industry, registered in Nevada, United States; its community exists to work on the industry’s common problems, never on any one member’s business [9].
The two layers are joined by one principle that GRA publishes as its trust rule: participation, endorsement, admission and legal power are four states that are never the same. An enquiry is not membership; an application is not acceptance; membership is not authority; and a name on a page is not an endorsement [10]. The digital layer is where those distinctions are made visible; the institutional layer is where they are enforced.
An earlier version of this page described a fully built digital community: member profiles, platform, council and working-group spaces, a sponsor portal, a public-authority space, a recognition hub and a listing of technical demonstrations. None of those spaces is open or on record, and they are withdrawn here. This page describes the model as GRA publishes it on its membership and participation and trust and integrity pages.
Why a risk community needs both layers
Systemic risk is a problem no single institution can measure, so the people who understand it have to work together. But an industry community also carries risks of its own: competitors coordinating where they should compete, members presenting participation as endorsement, sponsors buying influence over findings, and a digital space that excludes the people most exposed. A community model is useful only if it is designed against those failures from the start [11, 12].
The digital divide is the first of them. The International Telecommunication Union estimates that about 6 billion people use the internet in 2025, three quarters of the world’s population, while 2.2 billion remain offline, 96% of them in low- and middle-income countries [6]. Use is 94% in high-income countries but 23% in low-income ones, 85% in urban areas but 58% in rural ones, and 77% among men against 71% among women [6]. The countries and communities most exposed to uninsured climate and disaster losses are often the least connected. A community that lives only online would hear least from them.
The digital layer: open to anyone, today
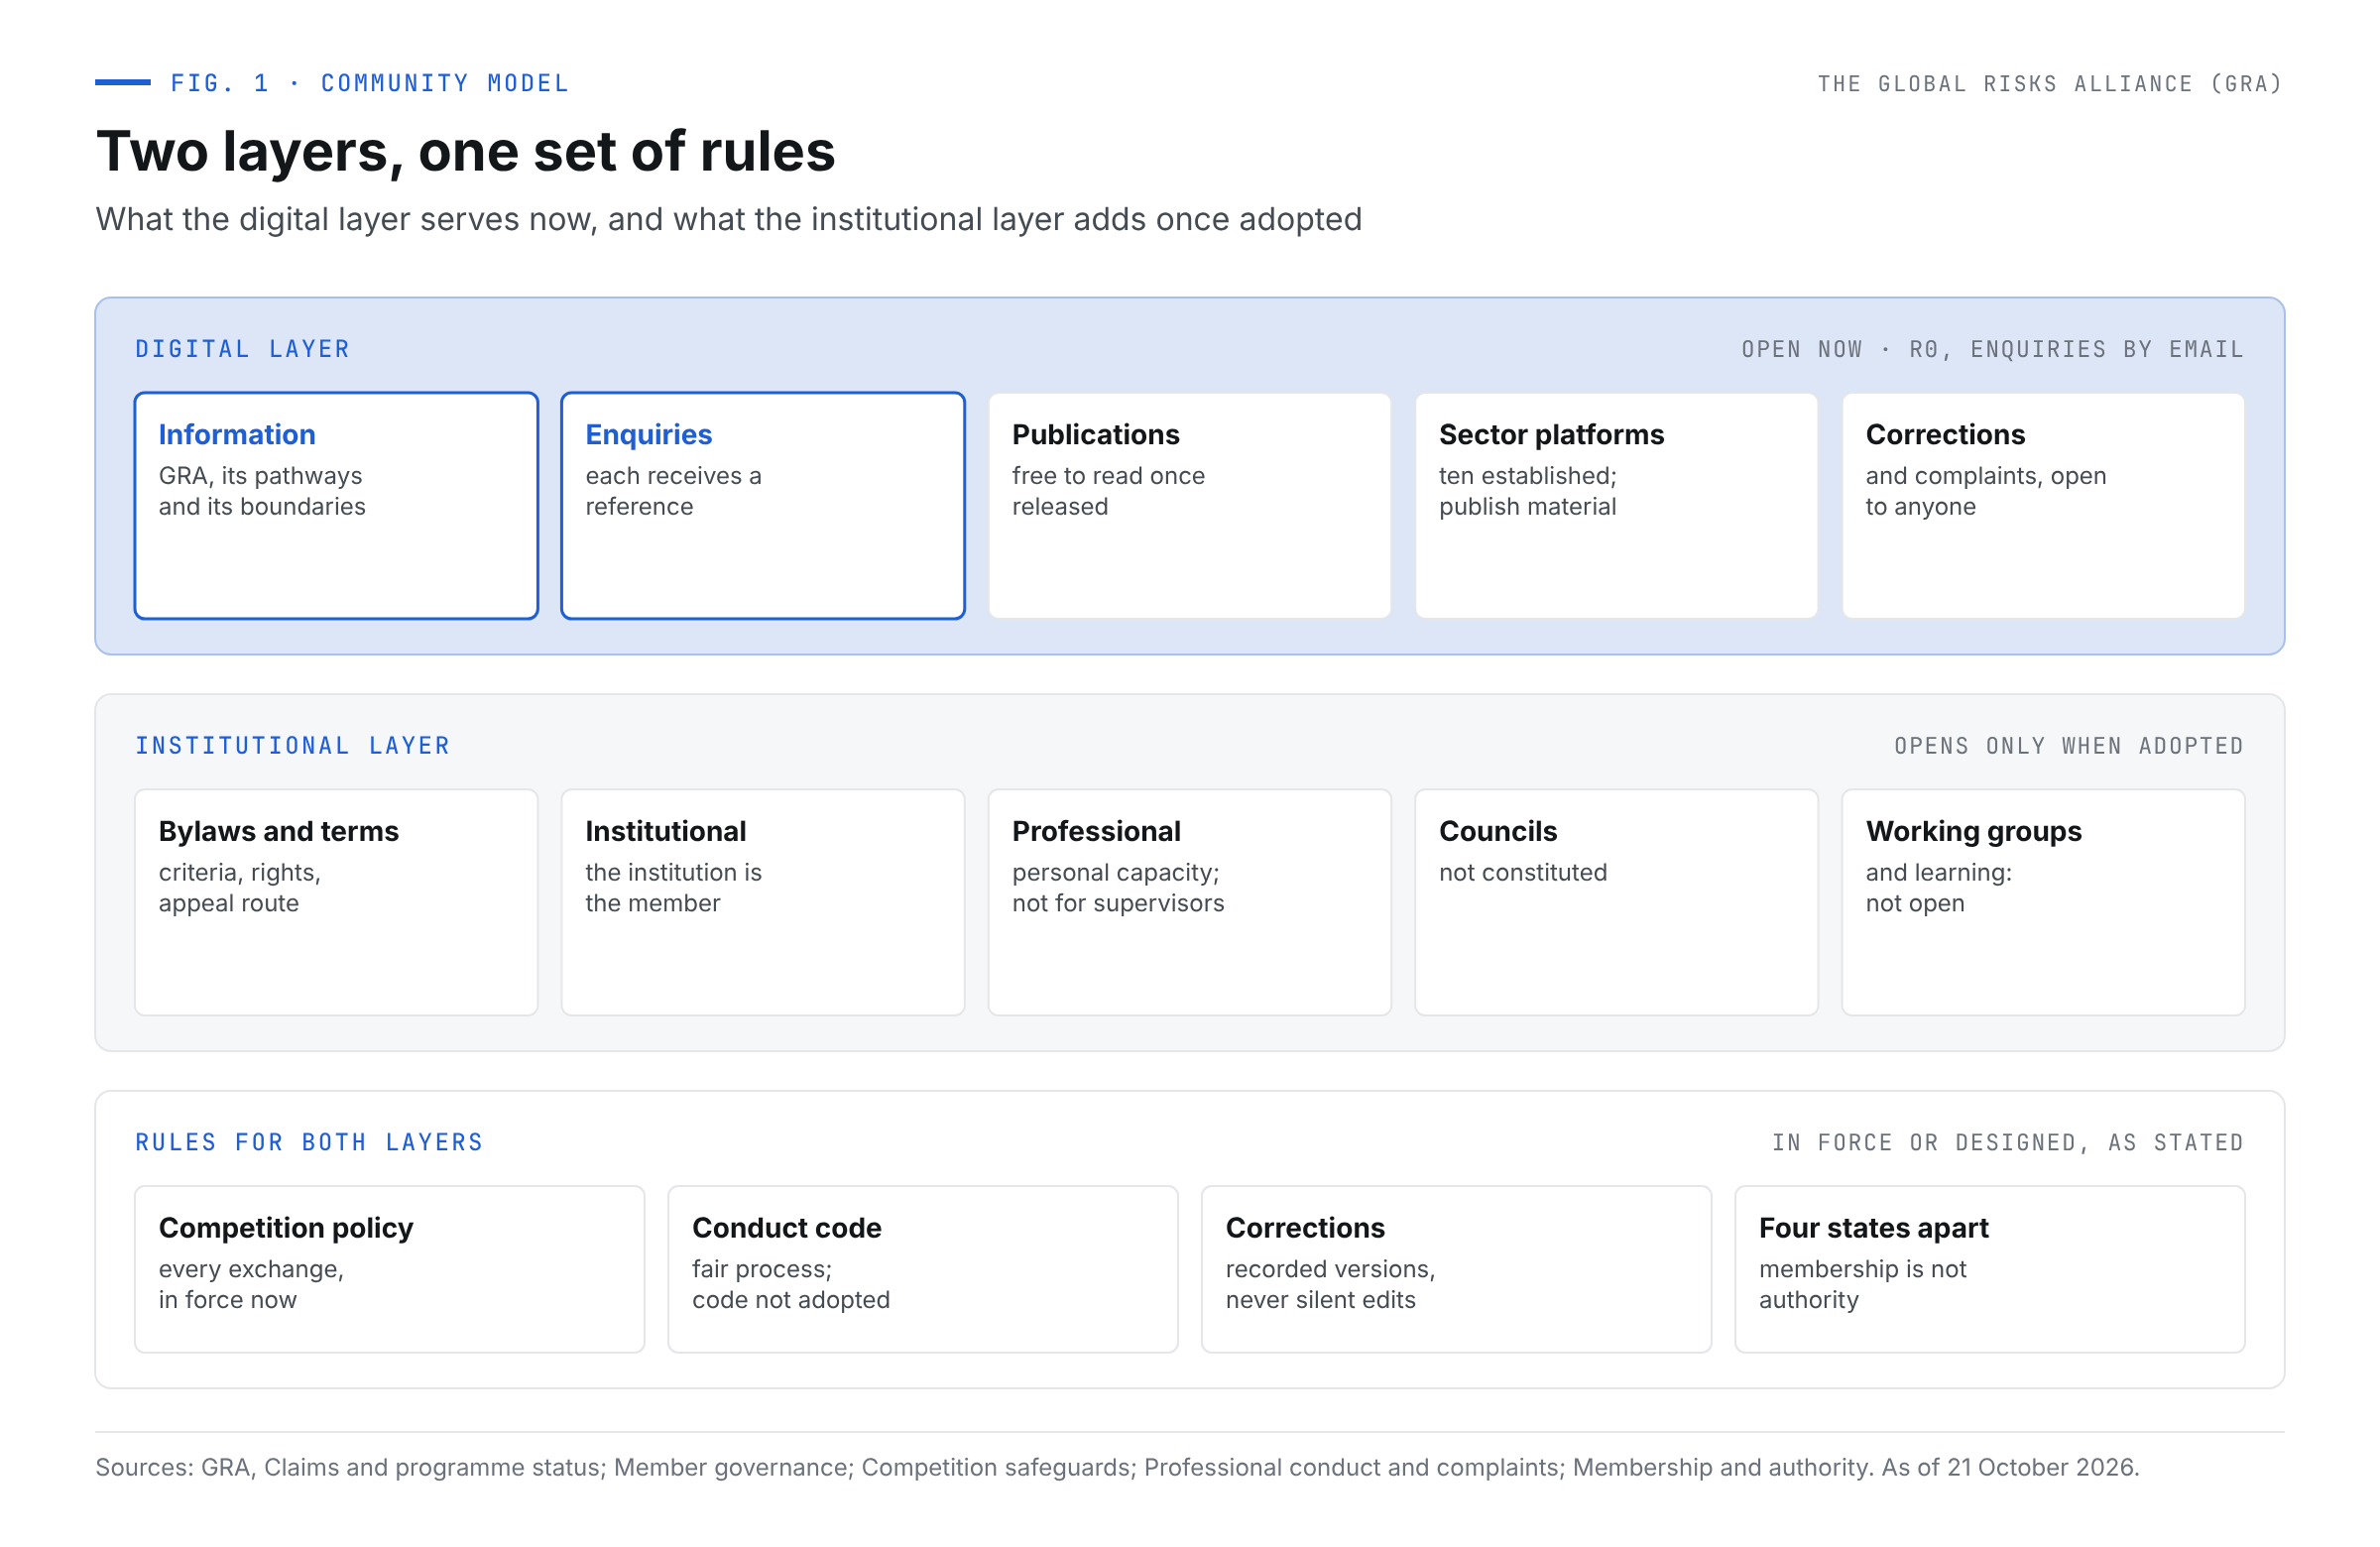
What GRA operates now is the digital layer. Information and enquiries are open at service level R0: anyone can understand GRA, its pathways and its boundaries, and anyone can send a question or register interest by email and receive a reference [1]. Ten sector platforms are established and publish material through the specialist financial network; publications and professional briefs are free to read once released; and correction, complaint and concern routes are open to anyone without membership or payment [1, 13, 4].
The digital layer follows the same claim discipline as everything GRA publishes. A capability, figure or status stated by an institution about itself is labelled as reported until someone independent has checked it against a record, and earlier statements without a dated, sourced record are withdrawn [1]. Events are listed only when verified, scheduled and approved; none is listed today [14].
The digital layer also has to be usable by everyone it serves. The current W3C recommendation, Web Content Accessibility Guidelines (WCAG) 2.2, was published on 12 December 2024 [15]; GRA publishes its own accessibility statement. Personal data in community work is handled under GRA’s privacy policy; for participants in the European Union, the General Data Protection Regulation has applied since 25 May 2018 [16].
The institutional layer: records first, then rights
Member governance will follow GRA’s bylaws and membership terms once they are adopted. The bylaws set the classes of member, if any, and which decisions, if any, members take; the membership terms set criteria, contributions, obligations, rights to leave and the appeal route, and are published before applications open; and a written competition policy governs how members meet [2]. Members are designed to have participation in platforms and working groups, access to learning and published work, a fair process for complaints and appeals, and voting only where the bylaws authorise it. They are designed to owe declarations of conflicts, respect for confidentiality and data rights, compliance with the competition rules, and never presenting participation as an endorsement or a licence [2].
Membership is designed in two forms. In institutional membership, the institution is the member, acting through authorised representatives: banks, insurers and reinsurers, asset owners and managers, development lenders, market infrastructure providers and fintech firms providing financial services [17]. In professional participation, actuaries, risk managers, quantitative analysts, economists, engineers and model validators take part in a personal capacity, with no right to speak for their employer [18]. Supervisors, regulators and central banks are not members; public servants take part in open GRA work only in their institutional role [17]. Terms are not adopted, applications are not open, and no fee is published or charged [17].
One set of conduct rules for both layers
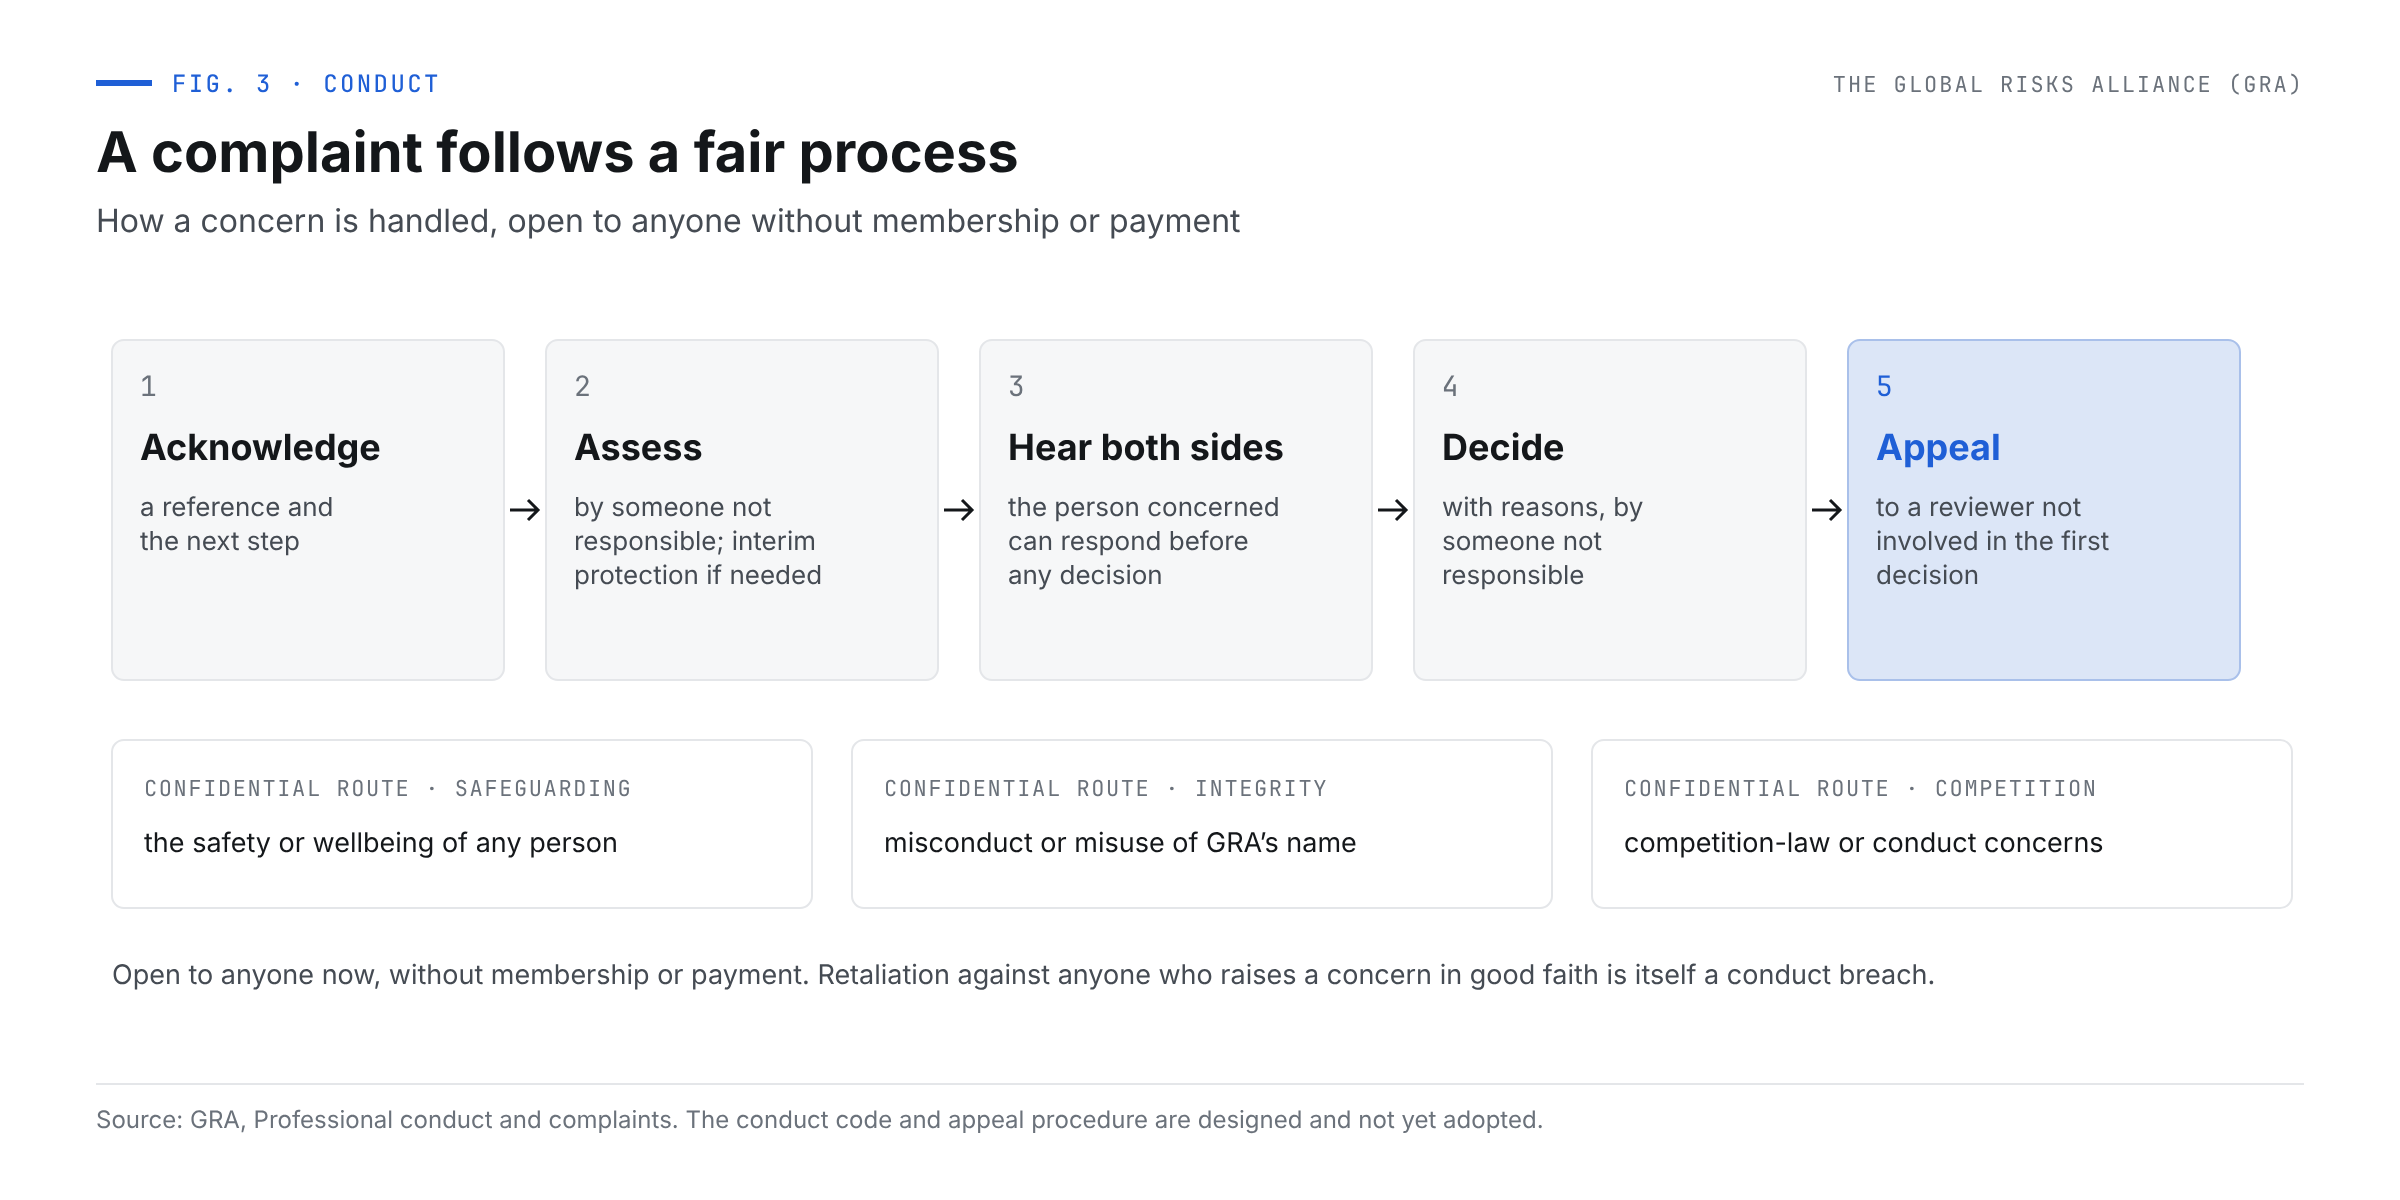
Professional conduct is designed to apply in every space, digital or institutional. Participants commit to declare conflicts and step back where a conflict bears on a decision, respect confidentiality and others’ data rights, follow the competition safeguards, never present participation as an endorsement, a licence or regulatory standing, treat others with respect and without harassment or discrimination, and never speak for GRA, a consortium or a public authority without authority to do so [4]. Safeguarding, integrity and competition concerns each have their own confidential route, and retaliation against anyone who raises a concern in good faith is itself a conduct breach [4].
A complaint follows a fair process: an acknowledgement with a reference, an assessment by someone not responsible for the matter, a hearing of both sides, a decision with reasons by someone not responsible for the contested matter, and an appeal to a reviewer not involved in the first decision [4]. The complaint route is open to anyone now; the conduct code and appeal procedure are not yet adopted, and no sanction is described as in force until they are [4].
What may be shared, and what never is
A community of competitors needs information rules more than it needs features. Under GRA’s competition safeguards, permitted exchanges are published research, methods and public data, aggregated industry data in which no firm can be identified, and views on shared evidence gaps and research questions. Never exchanged are a member’s confidential or competitively sensitive information, firm-level current or future prices, terms, costs or plans, and views on how members should respond commercially [3]. The European Commission’s Horizontal Guidelines of July 2023 set out how such exchanges are assessed in EU competition law [19].
Sponsorship follows the same logic: funding buys no control. No sponsor or member may approve, delay or suppress a publication; funding grants no ownership of findings; the source of funding is published with the work; and a sponsor’s name on a GRA page endorses nothing [12].
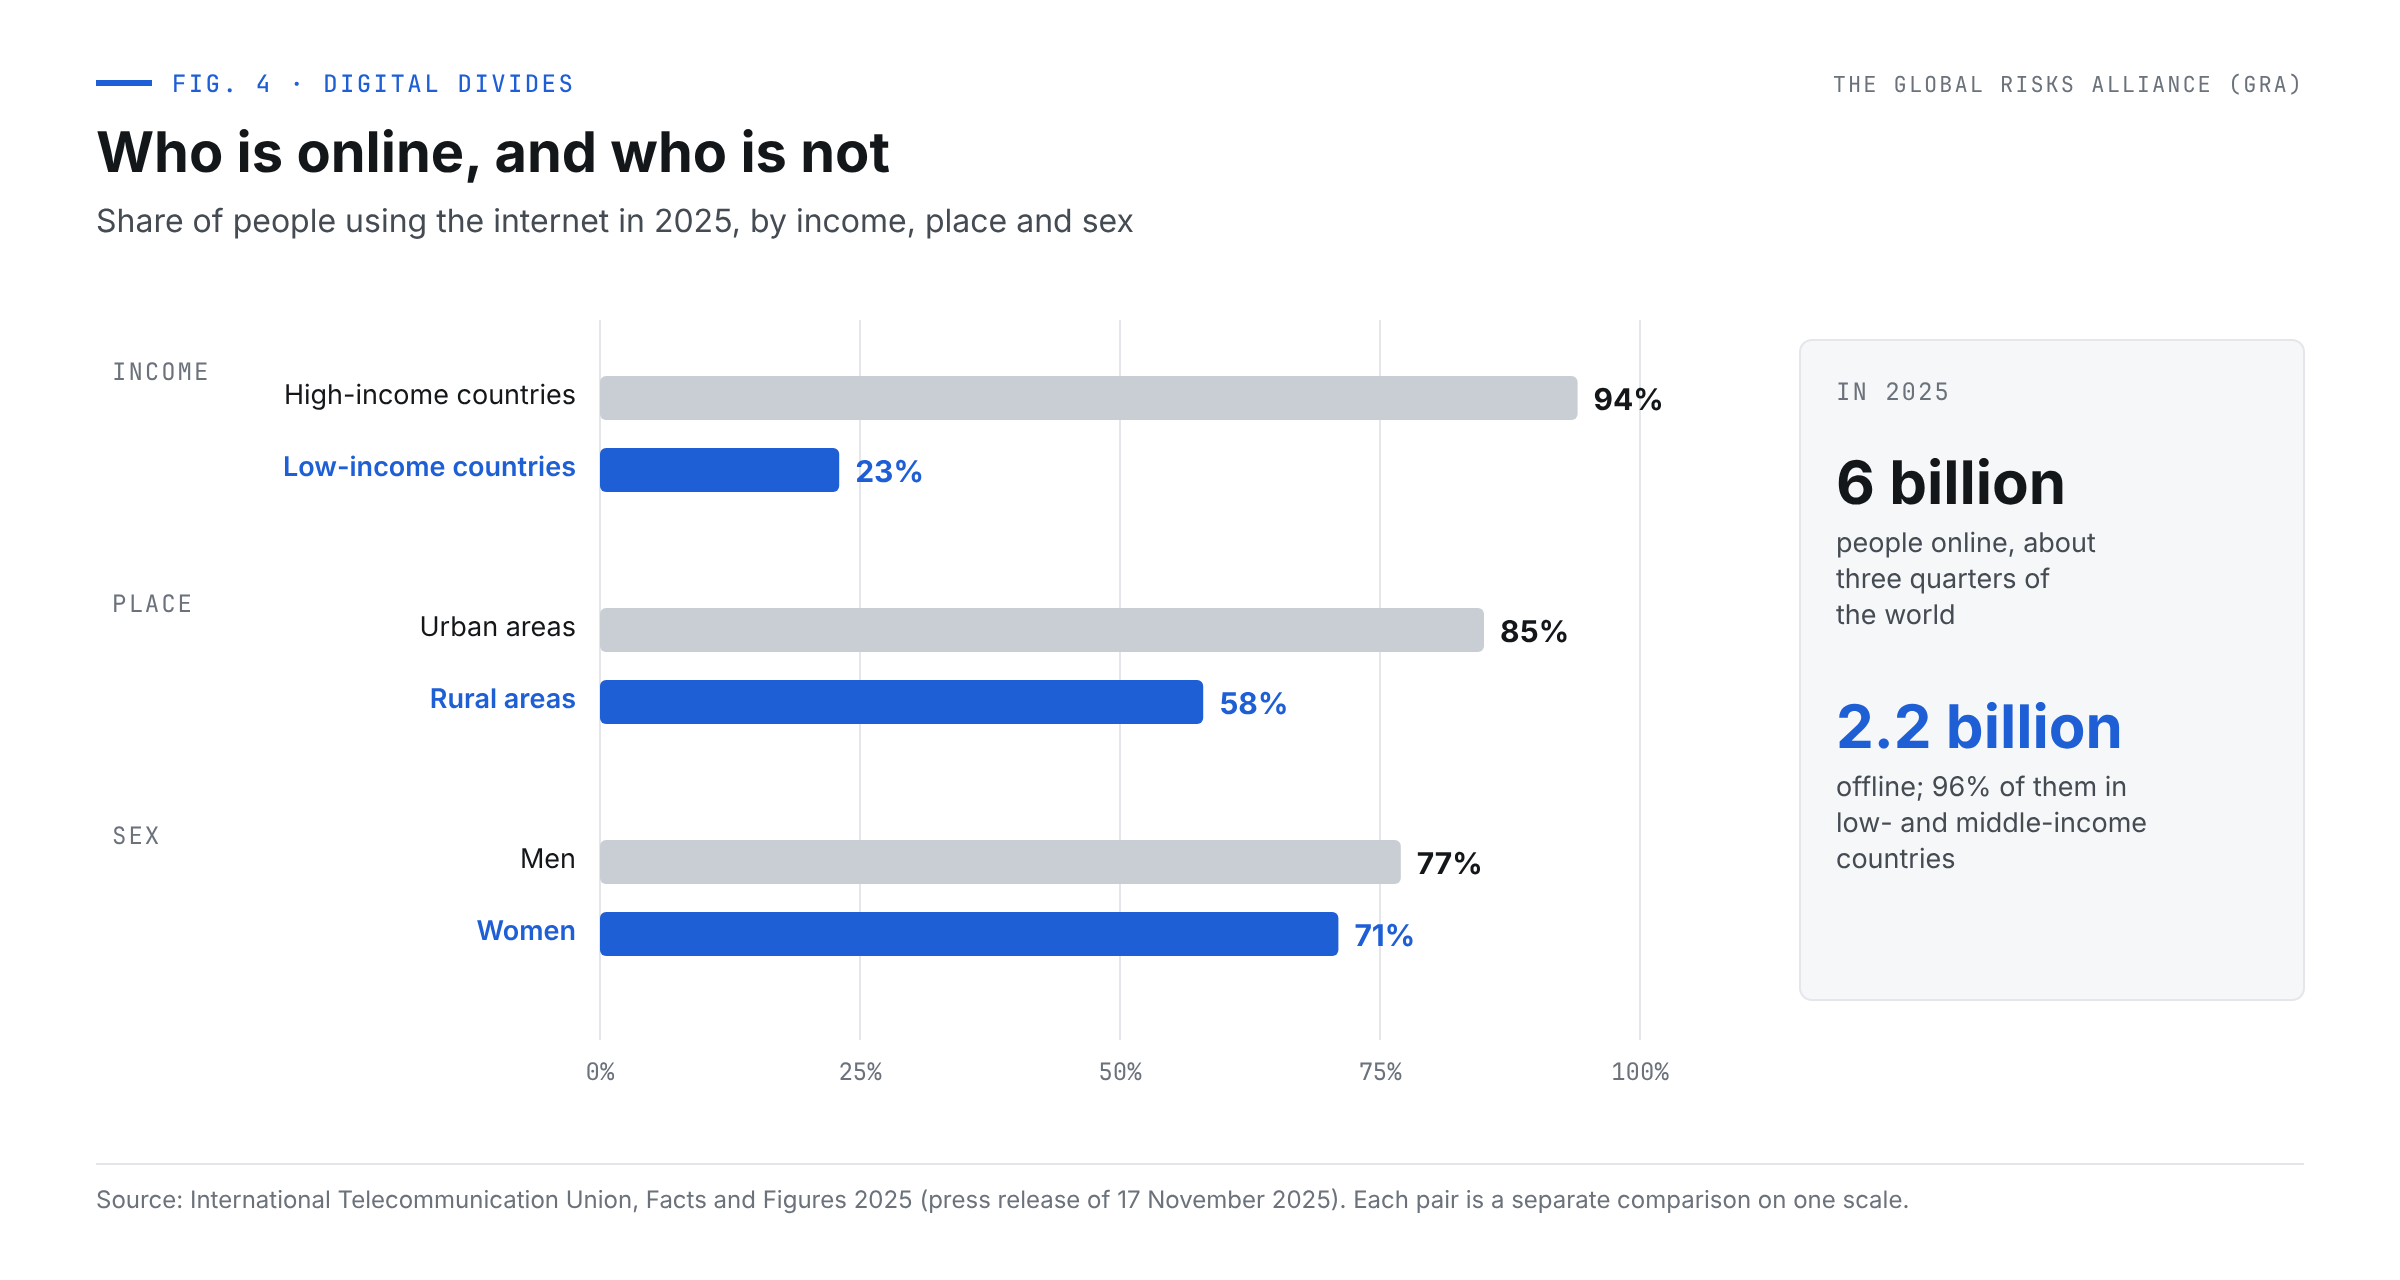
| Group | Online | Comparison group | Online |
|---|---|---|---|
| High-income countries | 94% [6] | Low-income countries | 23% [6] |
| Urban areas | 85% [6] | Rural areas | 58% [6] |
| Men | 77% [6] | Women | 71% [6] |
How participation is recorded
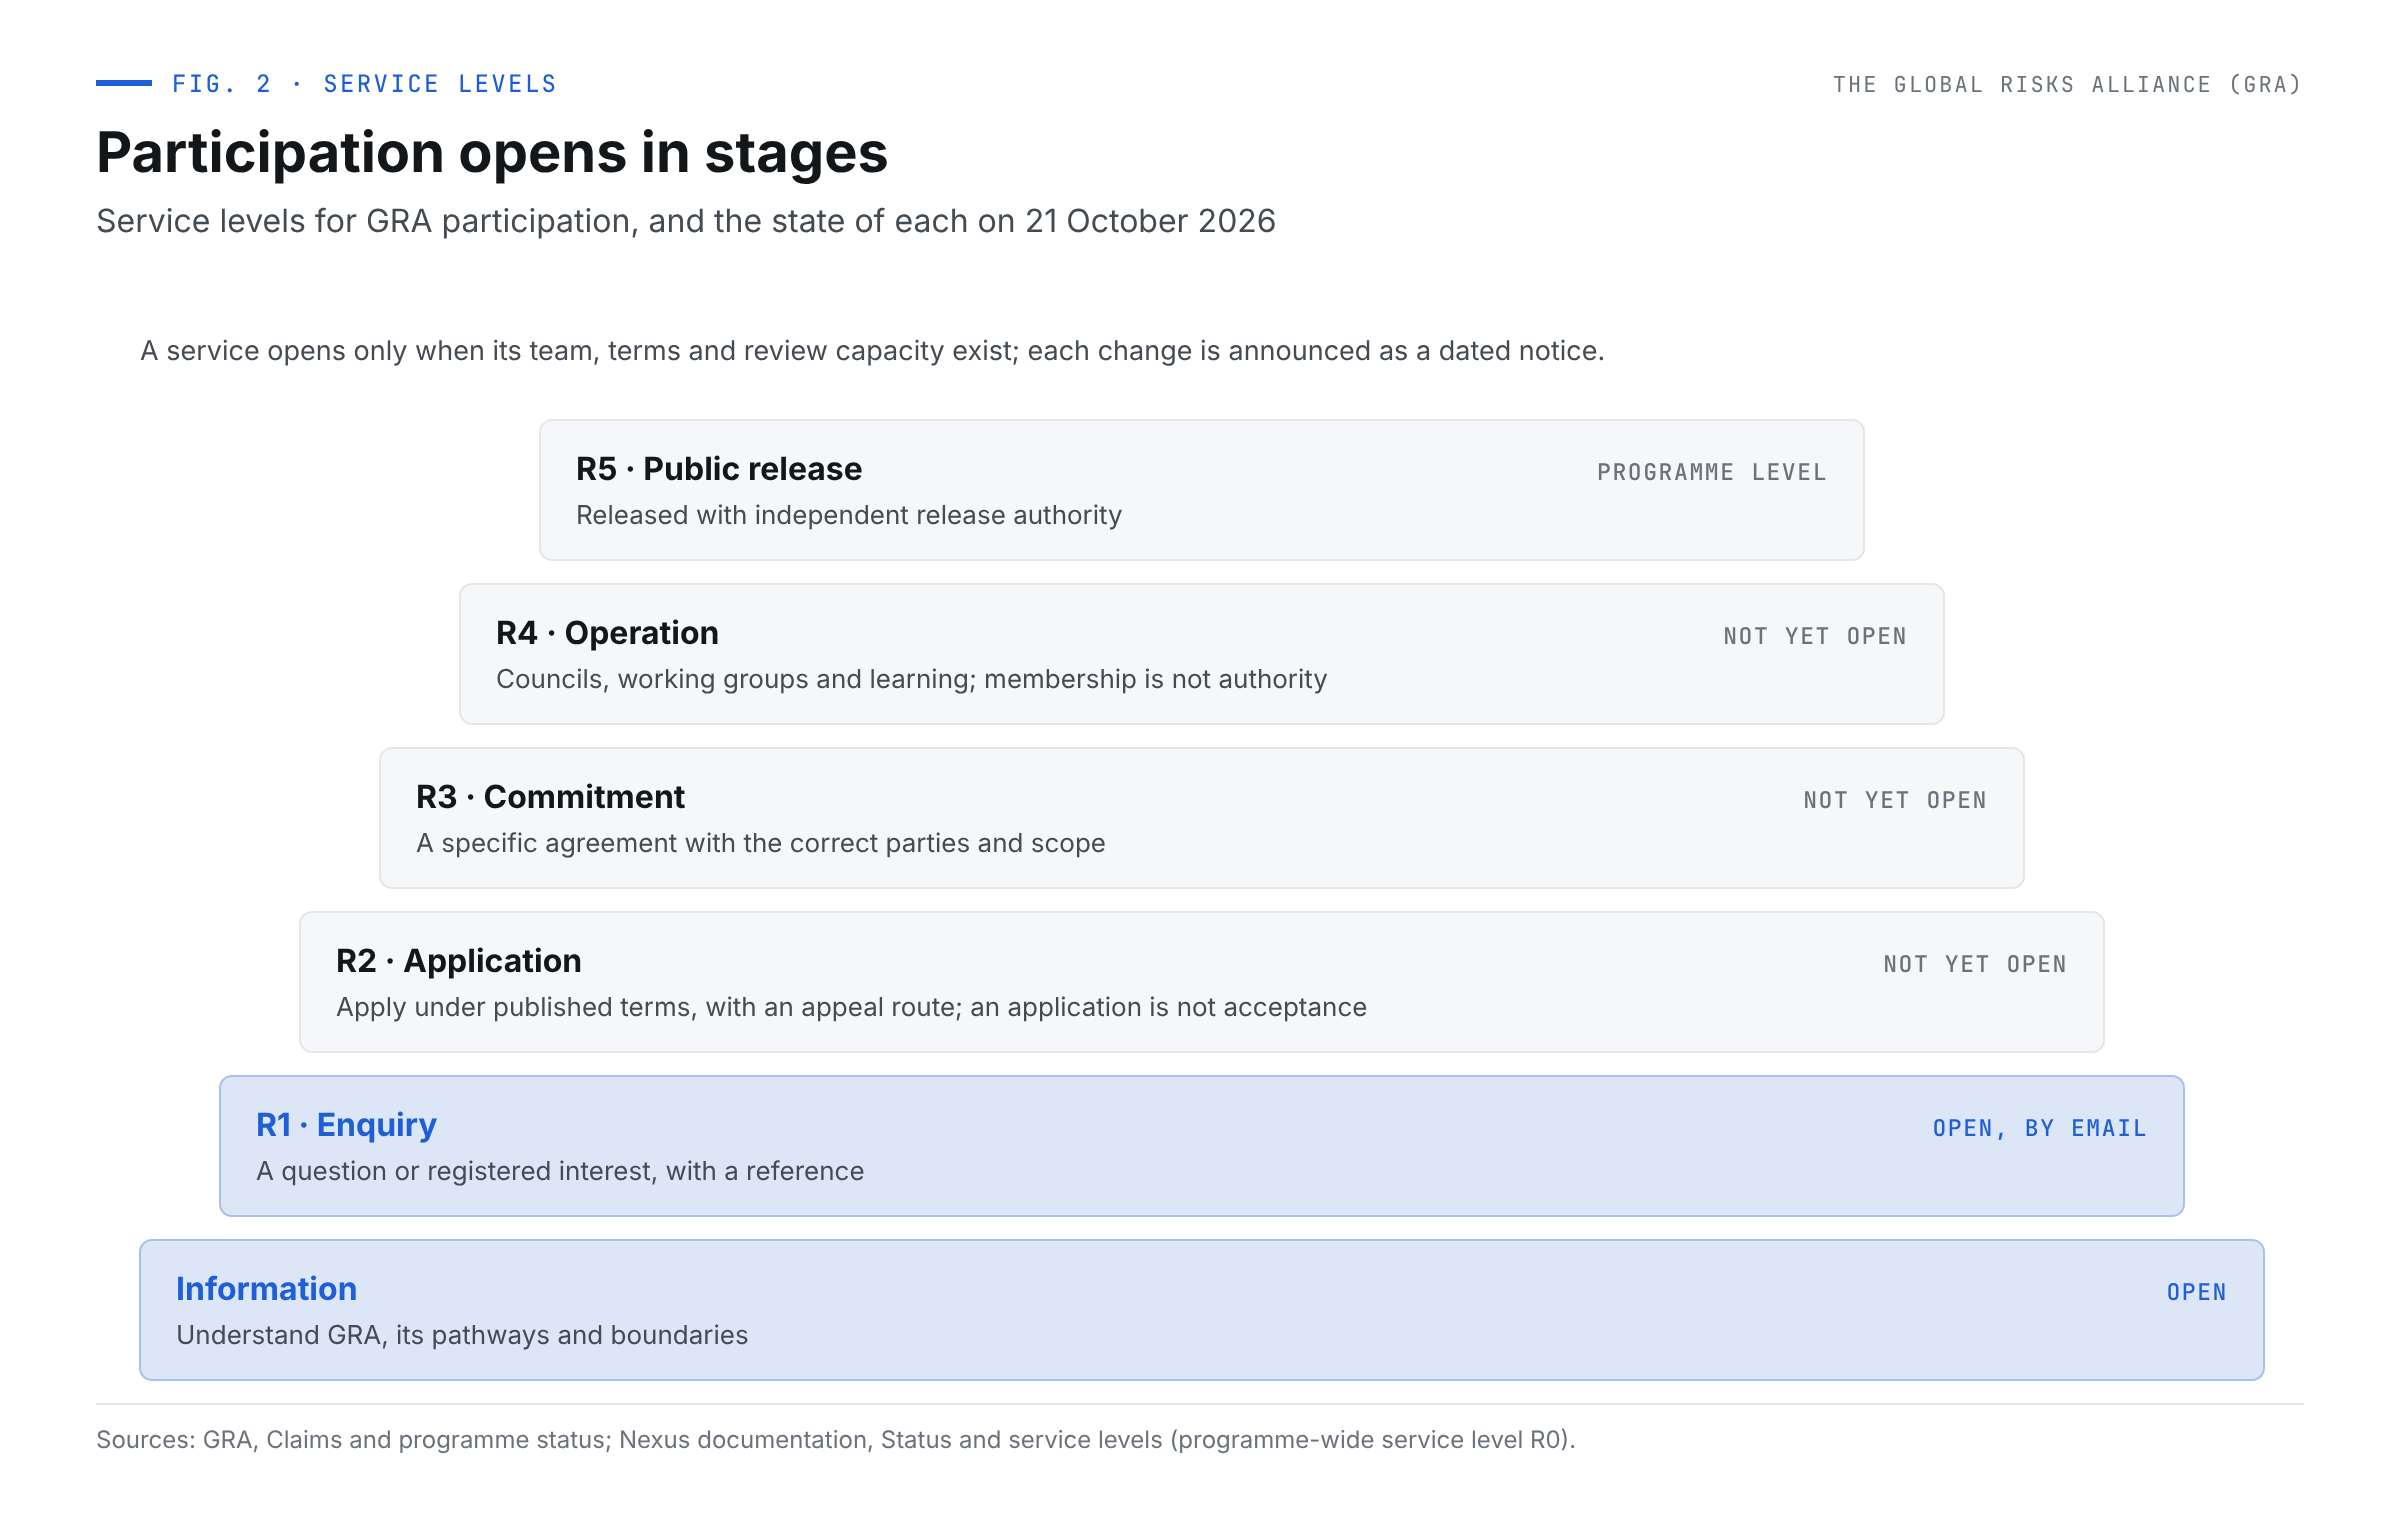
GRA keeps its own records of enquiries, applications, declarations and decisions, so that each step is its own step and can be checked [10]. Within the wider programme, who took part, in what capacity and under which agreement is recorded in the programme’s participation records, and in NXS-RLS (participants, agreements and handoffs). Public, client and partner delivery runs through NXS-POR (public, client and partner delivery), and authorisation and assurance through NXS-NSF (trust, authorization and assurance) [7].
The application of the annual programme, Nexus Universe, has its home at universe.nexus, ahead of its launch [8]. Online applications, contribution payments, computing allocations and event registration across the programme open only when their service team, terms and review capacity are in place [7].
The rules the community is designed against
The community model takes no regulatory role. It is designed so that what happens in it can withstand the rules that already apply to its participants.
| Year | Rule | Status and relevance |
|---|---|---|
| 2018 | EU General Data Protection Regulation, Regulation (EU) 2016/679 | Applies since 25 May 2018; personal data of participants [16] |
| 2023 | EU Horizontal Guidelines | Published 21 July 2023; information exchange between competitors [19] |
| 2024 | WCAG 2.2, W3C Recommendation | Version of 12 December 2024; accessibility of digital content [15] |
| 2025 | EU Digital Operational Resilience Act (DORA) | Applies since 17 January 2025 to 20 types of financial entities and ICT providers whose staff take part [20] |
What is changing
- Connectivity is not the same as participation. Use is rising, but quality and affordability gaps keep the least connected out of online-only communities [6].
- Accessibility as a baseline. WCAG 2.2 adds criteria that digital communities must meet for users with disabilities [15].
- Information exchange under scrutiny. Competition authorities pay closer attention to how competitors share data, including through digital platforms [19].
- Verified claims. Labelling a claim as reported or verified is becoming the honest default for institutional communities [1].
GRA’s community within the programme
GRA’s community is separate from the participation routes of the Nexus programme, and each institution keeps its own. The Global Centre for Risk and Innovation (GCRI) describes how institutions join a National Nexus programme through the National Nexus Consortium (NNC) and how experts join the National Working Groups. The Global Risks Forum (GRF) describes its own membership and how to participate in its leadership and dialogue. GRA reads risk evidence for finance and is the finance and insurance readiness interface of the programme; membership of GRA confers no role in any consortium [21, 17].
Boundaries. What this page does not claim: GRA’s membership terms, bylaws on membership, conduct code and appeal procedure are not adopted; councils are not constituted; working groups, learning and event registration are not open; information and enquiries are. Membership confers no authority, endorsement, regulatory standing, data access or influence over findings. GRA does not lend, underwrite, rate, invest, advise on or arrange transactions. GCRI does not regulate or certify, and GRF does not regulate, finance or procure.
Questions and answers
Can I join the GRA community online now?
You can use the digital layer now: read GRA’s pages and publications, send an enquiry or register interest by email and receive a reference. Membership applications open only when terms are adopted and a team can review them.
Do I need to be a member to raise a complaint or correct an error?
No. Anyone can raise a complaint, a concern or a possible error without membership or payment, and receives a reference and the name of the next step.
Can supervisors join the community?
Supervisors, regulators and central banks are not members. Public servants may take part in open GRA work only in their institutional role and under their own institution’s rules.
Can members share data with each other through the community?
Only published research, public data and aggregated data in which no firm can be identified. A member’s confidential or competitively sensitive information is never exchanged.
Will my name appear on a GRA page?
Only with consent and a current permission record. A name on a GRA page is not an endorsement by GRA, or of GRA, and participation may not be presented as a licence or qualification.
Glossary
- Digital layer: GRA’s public pages, publications and enquiry, correction and complaint routes, open to anyone.
- Institutional layer: Bylaws, membership terms, councils, platforms, working groups and learning, open to members once adopted.
- Service level: The stage at which a service operates, from R0, information, to R5, public release.
- Authorised representative: A person named by a member institution to take part on its behalf.
- Personal capacity: Taking part on one’s own expertise, without speaking for an employer.
- Reported claim: A statement an institution makes about itself, labelled apart from an independently verified one.
Further reading across the network
- Membership and participation
- Member governance
- Professional conduct and complaints
- Membership and authority
- Claims and programme status
- Competition safeguards
- Programme status at GCRI
- Status and service levels in the Nexus documentation
References
- The Global Risks Alliance (2026). Claims and programme status. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Member governance. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Competition safeguards. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Professional conduct and complaints. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Corrections and updates. Accessed 2026-10-21.
- International Telecommunication Union (2025). Facts and Figures 2025: connecting the world and beyond. Accessed 2026-10-21.
- The Global Centre for Risk and Innovation (Nexus documentation) (2026). Status and service levels. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Universe finance-readiness programme. Accessed 2026-10-21.
- The Global Risks Alliance (2026). U.S. business-league identity. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Membership and authority. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Antitrust and competition. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Conflicts, sponsors and neutrality. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Publications and professional briefs. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Events and professional dialogues. Accessed 2026-10-21.
- World Wide Web Consortium (W3C) (2024). Web Content Accessibility Guidelines (WCAG) 2.2. Accessed 2026-10-21.
- European Commission (2026). Legal framework of EU data protection: the General Data Protection Regulation. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Institutional members. Accessed 2026-10-21.
- The Global Risks Alliance (2026). Professional participation. Accessed 2026-10-21.
- European Commission, Directorate-General for Competition (2023). Horizontal block exemptions and the Horizontal Guidelines (OJ C 259, 21 July 2023). Accessed 2026-10-21.
- European Insurance and Occupational Pensions Authority (EIOPA) (2026). Digital Operational Resilience Act (DORA). Accessed 2026-10-21.
- The Global Risks Alliance (2026). GRA in the Consortium. Accessed 2026-10-21.
Editorial record
Facts and states are given as of 21 October 2026. This page is reviewed at least every 180 days and whenever membership terms, the conduct code or a service level changes. It replaces an earlier version whose member profiles, platform and council spaces, sponsor portal, public-authority space, recognition hub and listing of technical demonstrations are not open or on record; they are withdrawn here.
Published by the GRA editorial desk under the editorial integrity policy. To report an error or request a correction, use the corrections and updates route; corrections are dated and listed with the page.